
Automotive Zero-Day Vulnerabilities
VIEW DATABASEThe Criticality of Zero-Day Vulnerabilities Beyond Known Threats
Zero-day vulnerabilities currently have no vendor patch solution, but their exploitability has already been confirmed. What does this mean to organizations and enterprises?
Potential for Serious Damage
Confirmed zero-day vulnerabilities empower malicious actors to exploit them to execute attacks that could have dire consequences.
Lack of Defense
In the absence of a solution, attackers have ample time to exploit zero-day vulnerabilities repeatedly.
Wide-Ranging Impact
Given that the same open-source software and modules are utilized across multiple ECUs, zero-day vulnerabilities can affect numerous components.
Real-World Exploits Triggered by Zero-Day Vulnerabilities
at Pwn2Own Vancouver
Real-World Exploit Intelligence
The Latest Automotive Zero-Day Vulnerability Database
The following is a list of automotive vulnerabilities discovered by researchers through Trend Zero Day Initiative™ (ZDI) that are yet to be publicly disclosed. This initial list comprises zero-day vulnerabilities discovered at Pwn2Own Automotive, hosted by VicOne with Trend ZDI. For each vulnerability, the affected vendor has been contacted and is expected to develop a patch. These vulnerabilities are handled according to the Trend ZDI Disclosure Policy. The zero-day identifier of a vulnerability refers to the candidate (CAN) number assigned to the vulnerability by Trend ZDI.
| Zero-day identifier | CVE | Category | Impact |
|---|---|---|---|
| ZDI-CAN-26337 | Not yet assigned | Electric Vehicle Chargers | Compromise the integrity of downloaded information. |
| ZDI-CAN-26307 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26283 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of service account. |
| ZDI-CAN-26316 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26322 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26312 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26357 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-26331 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26350 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26324 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26290 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of service account. |
| ZDI-CAN-26286 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of service account. |
| ZDI-CAN-26285 | Not yet assigned | In-Vehicle Infotainment (IVI) | Bypass authentication on the system. |
| ZDI-CAN-26284 | Not yet assigned | In-Vehicle Infotainment (IVI) | Bypass authentication on the system. |
| ZDI-CAN-26318 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26311 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26300 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26327 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26297 | Not yet assigned | Operating System | Execute code in the context of root. |
| ZDI-CAN-26348 | Not yet assigned | Operating System | Disclose sensitive information. |
| ZDI-CAN-26305 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26330 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26332 | Not yet assigned | Electric Vehicle Chargers | Firewall Bypass. |
| ZDI-CAN-26295 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26339 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-26340 | Not yet assigned | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-26334 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-26333 | Not yet assigned | Electric Vehicle Chargers | Compromise the integrity of downloaded information. |
| ZDI-CAN-26292 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26325 | Not yet assigned | Electric Vehicle Chargers | Escalate privileges and execute arbitrary code in the context of root. |
| ZDI-CAN-26317 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26306 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26346 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26349 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26351 | Not yet assigned | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-26352 | Not yet assigned | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-26353 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26354 | Not yet assigned | Electric Vehicle Chargers | Compromise the integrity of downloaded information. |
| ZDI-CAN-26359 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26314 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26299 | Not yet assigned | Electric Vehicle Chargers | Compromise the integrity of downloaded information. |
| ZDI-CAN-26288 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26328 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26355 | Not yet assigned | In-Vehicle Infotainment (IVI) | Compromise the integrity of downloaded information. |
| ZDI-CAN-26294 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26315 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26313 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26321 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26338 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23150 | CVE-2024-23920 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23300 | CVE-2024-23921 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23187 | CVE-2024-29207 | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-23186 | CVE-2024-29208 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-22939 | CVE-2024-23922 | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-23184 | CVE-2024-23938 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23189 | CVE-2024-23937 | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-22945 | CVE-2024-23923 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23238 | CVE-2024-23933 | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-23244 | CVE-2024-26003 | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-23303 | CVE-2024-26005 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23157 | CVE-2024-7537 | Operating System | Execute code in the context of root. |
| ZDI-CAN-22994 | CVE-2024-23934 | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-23196 | CVE-2024-23958 | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-23194 | CVE-2024-23959 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23105 | CVE-2024-23924 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23101 | CVE-2024-23928 | In-Vehicle Infotainment (IVI) | Compromise the integrity of downloaded information. |
| ZDI-CAN-23301 | CVE-2024-23929 | In-Vehicle Infotainment (IVI) | Create arbitrary files on affected installations. |
| ZDI-CAN-23302 | CVE-2024-23930 | In-Vehicle Infotainment (IVI) | Create a denial-of-service condition on the system. |
| ZDI-CAN-23249 | CVE-2024-23935 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23158 | CVE-2024-25995 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23239 | CVE-2024-26000 | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-23304 | CVE-2024-26001 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23305 | CVE-2024-26002 | Electric Vehicle Chargers | Escalate privileges and execute arbitrary code in the context of root. |
| ZDI-CAN-23102 | CVE-2024-23960 | In-Vehicle Infotainment (IVI) | Bypass signature validation mechanism. |
| ZDI-CAN-23306 | CVE-2024-23961 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23190 | CVE-2024-7538 | Operating System | Execute code in the context of root. |
| ZDI-CAN-23195 | CVE-2024-7539 | Operating System | Execute code in the context of root. |
| ZDI-CAN-23193 | Not yet assigned | Operating System | Execute code in the context of root. |
| ZDI-CAN-23246 | CVE-2024-23962 | In-Vehicle Infotainment (IVI) | Disclose sensitive information. |
| ZDI-CAN-23312 | CVE-2024-23963 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23230 | CVE-2024-23967 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23241 | CVE-2024-23957 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23245 | CVE-2024-24736 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23221 | CVE-2024-25996 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23222 | CVE-2024-23968 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23313 | CVE-2024-23969 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23185 | CVE-2024-23972 | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-23225 | CVE-2024-26288 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23320 | CVE-2024-25998 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23321 | CVE-2024-25997 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23229 | CVE-2024-23970 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23317 | CVE-2024-23971 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23226 | CVE-2024-24731 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23151 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-23318 | CVE-2024-29206 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23223 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
Want to know if you've been impacted?
Contact us to assess risks →
Gain Advantage With Unique Zero-Day Insights
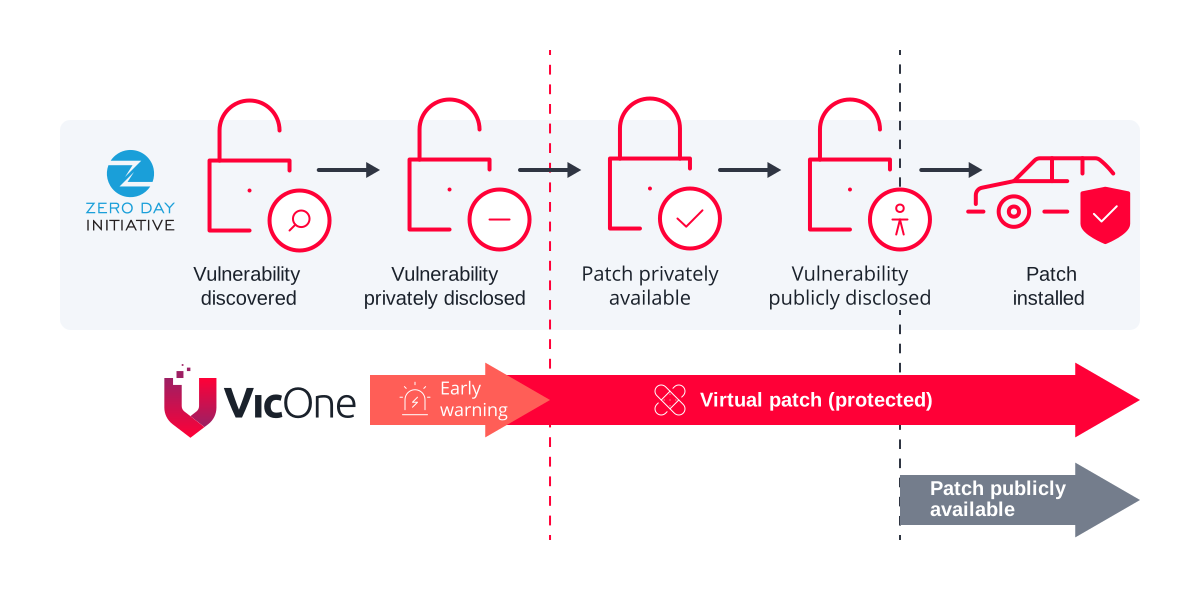
VicOne's best-in-class automotive threat intelligence includes early access to vital information on automotive zero-day vulnerabilities:
- Gain Early Warning: We empower OEMs, suppliers, and stakeholders with risk assessment capabilities. We will assess whether your components or software versions are impacted by zero-day vulnerabilities ahead of competitors, allowing for better resource allocation during planning. This approach complies with the spirit of ISO/SAE 21434 by helping you monitor newly emerged vulnerabilities.
- Gain Early Protection: We will evaluate how to collaborate with you based on attack tactics, techniques, and procedures to create effective virtual patches for safeguarding your system.
Want to know if you've been impacted?
Contact us to assess risks →
No. 1
in vulnerability discovery and disclosure since 2007*
5+ years
of partnership with Tesla for Pwn2Own, starting in 2017
*Source: Omdia Research, Quantifying the Public Vulnerability Market: 2024 Edition
More Insights Into Automotive Zero-Day Vulnerabilities From VicOne
GAIN INSIGHTS INTO AUTOMOTIVE CYBERSECURITY
Can a Robot Do Everything Right and Still Be Unsafe?
What a conversation between Boston Dynamics and VicOne reveals about how manipulated information can turn expected robot operation into an unsafe outcome
READ MORE →
VicOne Situational Awareness Report: 400 Cyber Incidents, with In-Vehicle Systems Most Affected in Q3 2026
VicOne's Q3 2026 Situational Awareness Report tracks where automotive cyber risk shifted: in-vehicle systems overtook enterprise IT as the most affected domain, Asia recorded a 36.8% rise in observed incidents, and ransomware activity spanned the full automotive value chain across 97 incidents.
READ MORE →
Sony Patches Seven XAV-9500ES Flaws That Could Have Enabled Device Compromise
Sony patched seven XAV-9500ES vulnerabilities affecting Wi-Fi, Bluetooth, and USB. VicOne examines the attack paths, potential impact, and next steps.
READ MORE →
Why Cybersecurity Is Essential to Safety Assurance for Physical AI
Physical AI can become unsafe even without experiencing conventional failures. Safety assurance must account for cyber manipulation of the inputs, models, commands, and systems that shape robot behavior.
READ MORE →