
自動車ゼロデイ脆弱性
データベースを見るゼロデイ脆弱性:既知の脅威を超えた深刻なリスク
ゼロデイ脆弱性とは、ベンダーによる修正パッチが提供されていないにもかかわらず、すでに悪用可能であることが確認されている脆弱性のことを指します。このような脆弱性は、企業や組織にとって深刻なリスクとなります。
深刻な被害の可能性
確認されたゼロデイ脆弱性は、サイバー攻撃者に悪用される可能性が高く、機密情報の流出や業務の中断など、企業や組織に甚大な被害をもたらす可能性があります。
防御策の欠如
ゼロデイ脆弱性に対するベンダーの修正パッチが提供されていない状況では、攻撃者は長期間にわたって脆弱性を悪用し続けることが可能となり、企業や組織は、その間、効果的な防御策を講じることが困難になります。
広範囲な影響
同一のオープンソースソフトウェアやモジュールが複数の電子制御ユニット(ECU)で使用されていることを考慮すると、1つのゼロデイ脆弱性が多数のコンポーネントに影響を及ぼす可能性があります。これにより、脆弱性の影響範囲が広がり、企業や組織全体のセキュリティリスクが増大します。
ゼロデイ脆弱性を悪用した
現実世界での攻撃事例
Pwn2Own Vancouverにて実証
現実世界での悪用情報
最新の自動車ゼロデイ脆弱性データベース
以下は、Trend Zero Day Initiative™ (ZDI)を通じて研究者により発見されたものの、まだ一般に公開されていない自動車関連の脆弱性のリストです。この初期リストは、VicOneとTrend ZDIが共同で主催するPwn2Own Automotiveにおいて発見されたゼロデイ脆弱性で構成されています。各脆弱性については、影響を受けるベンダーに通知がなされており、パッチの開発が期待されています。これらの脆弱性は、Trend ZDI 脆弱性開示ポリシーに従って取り扱われます。脆弱性のゼロデイ識別子は、Trend ZDIによって脆弱性に割り当てられた候補(CAN) 番号を指します。
| Zero-day identifier | CVE | Category | Impact |
|---|---|---|---|
| ZDI-CAN-26337 | Not yet assigned | Electric Vehicle Chargers | Compromise the integrity of downloaded information. |
| ZDI-CAN-26307 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26283 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of service account. |
| ZDI-CAN-26316 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26322 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26312 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26357 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-26331 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26350 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26324 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26290 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of service account. |
| ZDI-CAN-26286 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of service account. |
| ZDI-CAN-26285 | Not yet assigned | In-Vehicle Infotainment (IVI) | Bypass authentication on the system. |
| ZDI-CAN-26284 | Not yet assigned | In-Vehicle Infotainment (IVI) | Bypass authentication on the system. |
| ZDI-CAN-26318 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26311 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26300 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26327 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26297 | Not yet assigned | Operating System | Execute code in the context of root. |
| ZDI-CAN-26348 | Not yet assigned | Operating System | Disclose sensitive information. |
| ZDI-CAN-26305 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26330 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26332 | Not yet assigned | Electric Vehicle Chargers | Firewall Bypass. |
| ZDI-CAN-26295 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26339 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-26340 | Not yet assigned | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-26334 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-26333 | Not yet assigned | Electric Vehicle Chargers | Compromise the integrity of downloaded information. |
| ZDI-CAN-26292 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26325 | Not yet assigned | Electric Vehicle Chargers | Escalate privileges and execute arbitrary code in the context of root. |
| ZDI-CAN-26317 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26306 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26346 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26349 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26351 | Not yet assigned | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-26352 | Not yet assigned | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-26353 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26354 | Not yet assigned | Electric Vehicle Chargers | Compromise the integrity of downloaded information. |
| ZDI-CAN-26359 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-26314 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26299 | Not yet assigned | Electric Vehicle Chargers | Compromise the integrity of downloaded information. |
| ZDI-CAN-26288 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26328 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26355 | Not yet assigned | In-Vehicle Infotainment (IVI) | Compromise the integrity of downloaded information. |
| ZDI-CAN-26294 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-26315 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26313 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26321 | Not yet assigned | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-26338 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23150 | CVE-2024-23920 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23300 | CVE-2024-23921 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23187 | CVE-2024-29207 | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-23186 | CVE-2024-29208 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-22939 | CVE-2024-23922 | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-23184 | CVE-2024-23938 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23189 | CVE-2024-23937 | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-22945 | CVE-2024-23923 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23238 | CVE-2024-23933 | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-23244 | CVE-2024-26003 | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-23303 | CVE-2024-26005 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23157 | CVE-2024-7537 | Operating System | Execute code in the context of root. |
| ZDI-CAN-22994 | CVE-2024-23934 | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-23196 | CVE-2024-23958 | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-23194 | CVE-2024-23959 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23105 | CVE-2024-23924 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23101 | CVE-2024-23928 | In-Vehicle Infotainment (IVI) | Compromise the integrity of downloaded information. |
| ZDI-CAN-23301 | CVE-2024-23929 | In-Vehicle Infotainment (IVI) | Create arbitrary files on affected installations. |
| ZDI-CAN-23302 | CVE-2024-23930 | In-Vehicle Infotainment (IVI) | Create a denial-of-service condition on the system. |
| ZDI-CAN-23249 | CVE-2024-23935 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23158 | CVE-2024-25995 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23239 | CVE-2024-26000 | Electric Vehicle Chargers | Disclose sensitive information. |
| ZDI-CAN-23304 | CVE-2024-26001 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23305 | CVE-2024-26002 | Electric Vehicle Chargers | Escalate privileges and execute arbitrary code in the context of root. |
| ZDI-CAN-23102 | CVE-2024-23960 | In-Vehicle Infotainment (IVI) | Bypass signature validation mechanism. |
| ZDI-CAN-23306 | CVE-2024-23961 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23190 | CVE-2024-7538 | Operating System | Execute code in the context of root. |
| ZDI-CAN-23195 | CVE-2024-7539 | Operating System | Execute code in the context of root. |
| ZDI-CAN-23193 | Not yet assigned | Operating System | Execute code in the context of root. |
| ZDI-CAN-23246 | CVE-2024-23962 | In-Vehicle Infotainment (IVI) | Disclose sensitive information. |
| ZDI-CAN-23312 | CVE-2024-23963 | In-Vehicle Infotainment (IVI) | Execute code in the context of root. |
| ZDI-CAN-23230 | CVE-2024-23967 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23241 | CVE-2024-23957 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23245 | CVE-2024-24736 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23221 | CVE-2024-25996 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23222 | CVE-2024-23968 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23313 | CVE-2024-23969 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23185 | CVE-2024-23972 | In-Vehicle Infotainment (IVI) | Execute code in the context of the device. |
| ZDI-CAN-23225 | CVE-2024-26288 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23320 | CVE-2024-25998 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23321 | CVE-2024-25997 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23229 | CVE-2024-23970 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23317 | CVE-2024-23971 | Electric Vehicle Chargers | Execute code in the context of root. |
| ZDI-CAN-23226 | CVE-2024-24731 | Electric Vehicle Chargers | Execute code in the context of the device. |
| ZDI-CAN-23151 | Not yet assigned | Electric Vehicle Chargers | Bypass authentication on the system. |
| ZDI-CAN-23318 | CVE-2024-29206 | Electric Vehicle Chargers | Execute code in the context of service account. |
| ZDI-CAN-23223 | Not yet assigned | Electric Vehicle Chargers | Execute code in the context of the device. |
脆弱性の影響が懸念されますか?
リスク評価をご希望の場合は、こちらまでご連絡ください。 →
ゼロデイ脆弱性への知見による優位性の獲得
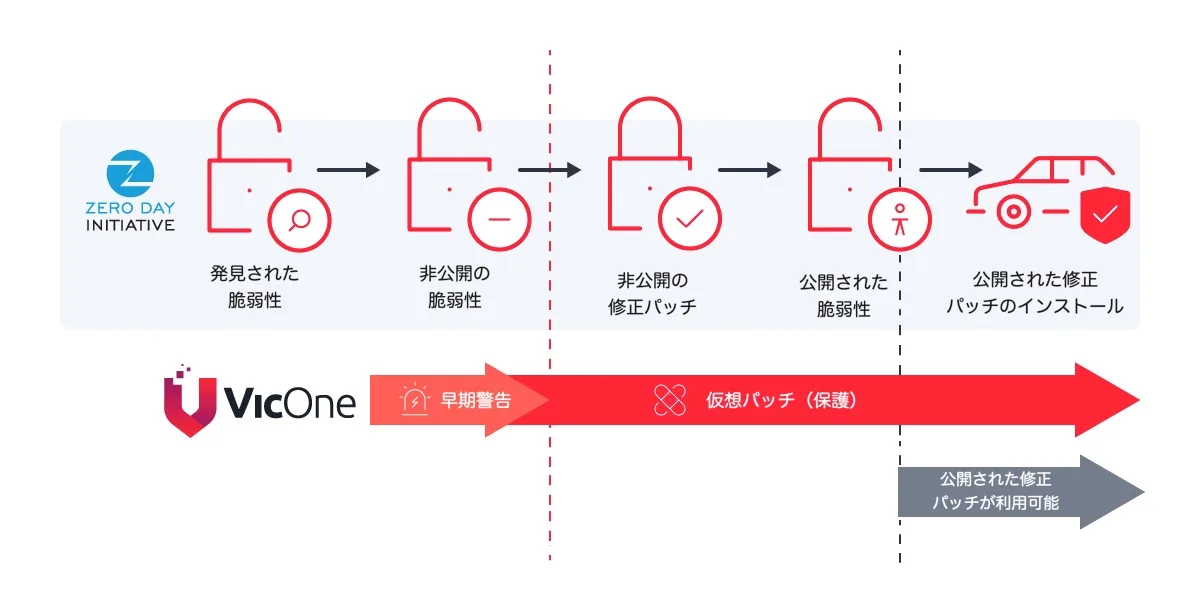
VicOneの業界最高水準の自動車スレットインテリジェンスでは、自動車のゼロデイ脆弱性に関する重要な情報に早期にアクセスできます。
- 早期警告の取得: VicOneは、OEMやサプライヤー、ステークホルダーの皆様にリスク評価能力を提供しています。競合他社に先駆けて、お客さまの製品に使用されているコンポーネントやソフトウェアのバージョンがゼロデイ脆弱性の影響を受けるかどうかを評価いたします。これにより、計画段階におけるリソース配分の最適化が可能となります。このアプローチは、新たに発見された脆弱性の監視に役立つため、ISO/SAE 21434の理念に準拠しています。
- 早期保護の実現: VicOneは、攻撃者の戦術、技術、手順を分析し、お客さまのシステムを保護するための効果的な仮想パッチを作成するための協力体制を確保しています。これにより、ゼロデイ脆弱性が悪用される前に、適切なセキュリティ対策を講じることが可能となります。
攻撃者の戦術と技術を攻撃の段階ごとに整理した自動車アタックマッピングもご覧ください。
脆弱性の影響が懸念されますか?
リスク評価をご希望の場合は、こちらまでご連絡ください。 →
第1位
2007年以降、脆弱性の発見と開示において第1位*
5年以上
2017年からTeslaとPwn2Ownで5年以上のパートナーシップ
*出典: Omdia Research, Quantifying the Public Vulnerability Market: 2024 Edition
VicOneからの自動車ゼロデイ脆弱性に関するさらなる知見
自動車サイバーセキュリティについてさらに詳しく
AIエージェントの判断から機器の動作までを守るフィジカルAIのサイバーセキュリティ
VicOneは、NVIDIAの「Open Agent Safety Platform」の取り組みに賛同し、AIエージェントの判断の安全性だけでなく、その判断が自動車やロボットの動作に及ぼす影響までをサイバーセキュリティの対象として捉えています。
続きを読む →
CRA適用の方向性を映すprEN 40000-1-4:ロボティクス業界が今備えるべきこと
prEN 40000-1-4の標準化を通じて見えてきたCRAの実際の運用と、ロボティクスメーカーが今から備えるべき対応をLAB R7が解説します。
続きを読む →
ヒューマノイドロボットが空港の現場へ:フィジカルAIを守るシミュレーション検証
羽田空港のような開かれた環境へのヒューマノイドロボット導入が進んでいます。シミュレーション段階での敵対的検証が、フィジカルAIにとって重要なセキュリティ対策のポイントとなる理由を解説します。
続きを読む →
車載ヘッドユニットが通信の中継点に:BADBOX関連マルウェアが悪用した正規のOTA更新
BADBOXに関連するマルウェアが、DoFunのAndroidヘッドユニットの正規のOTA更新機能とMQTTの保護の弱さを悪用し、利用者に気づかれないままインストールされていた手口をVicOneが解説します。
続きを読む →